THE SUMMARYAI-generated
Key Concepts:
- Post-Quantum Cryptography (PQC): Encryption methods designed to be secure against attacks from quantum computers.
- TLS 1.3: The latest version of the Transport Layer Security protocol, offering improved security and performance.
- Cipher Suite: A set of cryptographic algorithms used for key exchange, encryption, and message authentication.
- Cipher Rule: A defined set of acceptable cipher suites.
- Cipher Group: A collection of cipher rules.
- SSL Client Profile: A configuration object on a BIG-IP device that defines the SSL/TLS settings for client-side connections.
- Handshake Algorithm: The cryptographic process used to establish a secure connection between a client and a server.
- Virtual Server: A logical representation of a server on a BIG-IP device, used to manage and direct traffic.
Configuring a Virtual Server for Post-Quantum Cryptography
1. Current Configuration:
- The existing setup involves a web server behind a BIG-IP load balancer.
- The virtual server is configured on port 443 (HTTPS).
- An SSL client profile is in use, employing TLS 1.2 and standard classical handshakes.
- A Let's Encrypt certificate is installed and valid.
2. Transitioning to Post-Quantum Cryptography:
- The primary change involves modifying the handshake algorithm to use post-quantum encryption.
- This requires enabling TLS 1.3.
- Enabling TLS 1.3 necessitates defining a cipher rule and a cipher group.
3. Creating a Cipher Rule:
- A new cipher rule is created with default settings.
- Post-quantum algorithms are added to the rule.
- Default signature algorithms are also included.
- This process selects a range of cipher suites suitable for post-quantum cryptography and incorporates them into the rule set.
4. Creating a Cipher Group:
- A cipher group is created.
- The previously created cipher rule is selected and associated with the group.
- This action effectively groups the post-quantum cipher suites defined in the rule.
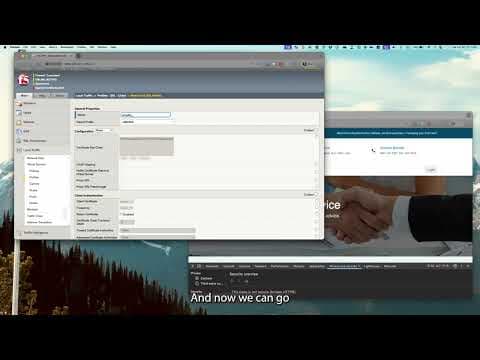
5. Creating an SSL Client Profile:
- A new SSL client profile is created, based on the existing profile to inherit settings like certificates.
- The profile is switched to "Advanced" mode to allow for specific configuration changes.
- TLS 1.3 is enabled by disabling the "no TLS 1.3" option.
- The cipher group created earlier (Arcadia group) is selected for use in this profile.
- Other settings from the base profile are retained.
6. Applying the New SSL Client Profile to the Virtual Server:
- The virtual server is modified to use the newly created SSL client profile (Arcadia TLS 13 PQC).
- The old SSL client profile is removed.
- The virtual server configuration is updated.
7. Verification:
- After refreshing the web page, the site appears the same to the user.
- However, inspecting the connection details reveals that TLS 1.3 is now in use.
- The encryption for the traffic remains the same, but the handshake process now utilizes post-quantum encryption algorithms.
8. Notable Quotes:
- "The difference when we moved to postquantum will be the handshake algorithm is going to be different."
9. Technical Terms:
- Cipher Suite: A combination of cryptographic algorithms used for key exchange, encryption, and message authentication. Examples include algorithms for key agreement (e.g., ECDHE, Kyber), encryption (e.g., AES, ChaCha20), and message authentication (e.g., SHA-256).
- Handshake: The process by which a client and server negotiate the cryptographic parameters for a secure connection. This includes agreeing on a cipher suite, exchanging keys, and authenticating each other.
10. Synthesis/Conclusion:
The video demonstrates the steps required to configure a BIG-IP virtual server to support post-quantum cryptography. This involves enabling TLS 1.3, creating custom cipher rules and groups that include post-quantum algorithms, and applying a new SSL client profile to the virtual server. The result is a web server that uses post-quantum encryption for the handshake process, enhancing its security against potential attacks from quantum computers, while maintaining compatibility with existing encryption methods for data transmission.
AI summaries can miss context or contain errors. Check important details against the original video.