Key Concepts
Third-party cookies, Privacy Sandbox APIs, CHIPS (Cookies Having Independent Partition State), Partitioned storage, Unpartitioned storage, Related Website Sets, Storage Access API, Federated Credential Management (FedCM), Identity payments, Embedded widgets, Cross-site tracking, Top-level context, Embedded context.
Detecting Reliance on Third-Party Cookies
- Initial Assessment: If a site doesn't embed external content, distribute cross-site widgets/scripts, or reuse session cookies across multiple sites, it might not rely on third-party cookies. However, due to the composable nature of the web, double-checking is crucial, especially for identity and payment solutions.
- User Flow Testing: The most effective method is to disable third-party cookies and meticulously test all user flows.
- Chrome DevTools: Disable third-party cookies temporarily via DevTools (Privacy and Security panel > Controls > Temporarily limit third-party cookies).
- Chrome Flags: Enable the "Test Third Party Cookie" flag in
chrome://flagsfor more fine-grained control.
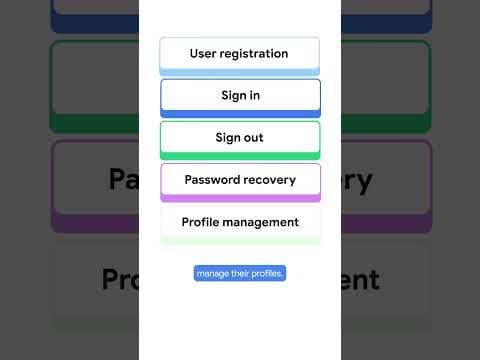
- Identity Checklist:
- Account creation
- Sign-in functionality (including personalized buttons)
- Sign-in status persistence across related domains
- Sign-out functionality and persistence
- Password recovery
- Payments Checklist:
- Checkout with third-party providers
- Adding, updating, and deleting payment methods
- Display of saved payment methods
- Rendering of personalized payment buttons
- Purchase completion even without preferred payment method display
- Payment fraud detection effectiveness
- Embedded Widgets Checklist:
- Chat widget access and session resumption across pages/domains
- Social media interactions (commenting, liking, reposting)
- Embedded content access (e.g., video players)
- Premium content access for subscribers
- Data dashboard widget loading and data display according to user preferences
- Dashboard navigation
Understanding the Context Pattern
- Third-Party Definition: A widget or script is considered third-party if embedded on a site different from where it's hosted, regardless of who implements it. Cookies set within such a widget, associated with the widget's domain, are also third-party.
- First-Party Cookies: If a widget is hosted on the same domain as the embedding page, its cookies are first-party. A third-party script can also set a first-party cookie using
document.cookie, associated with the embedding site's domain. - Top-Level vs. Embedded Context: When a user visits
site.example, it's the top-level context. Ifsite.exampleembeds a widget fromprovider.example, the widget operates in an embedded context. - Impact of Blocked Third-Party Cookies: If
streaming.examplesets a cookie upon user login (granting premium access) and then a player widget fromstreaming.exampleis embedded onblog.example, the widget cannot access the cookie when third-party cookies are blocked. This prevents the user from accessing premium content onblog.example.
Privacy Sandbox APIs: Solutions for a Cookieless Future
- Unpartitioned vs. Partitioned Storage:
- Unpartitioned: Storage accessible by a site in any context (top-level or embedded). Lacks isolation.
- Partitioned: Storage isolated and associated with the exact context it was set in.
- CHIPS (Cookies Having Independent Partition State):
- Functionality: Adds the
partitionedattribute to cookies, creating double-keyed cookies (by widget provider and embedding site). - Storage: CHIPS live in partitioned storage, with a separate cookie jar per top-level site.
- Accessibility: Only accessible from the same context (widget and embedding site).
- Use Cases: Site-specific settings for chat widgets or payment dashboards.
- Browser Support: Supported by most major browsers, with others actively working on implementation.
- Functionality: Adds the
- Related Website Sets:
- Functionality: Allows declaring relationships between multiple owned sites.
- Access: Grants limited third-party cookie access within the set.
- Use Cases: In-house identity services or payment link services residing on different domains.
- Implementation: Declare a related website set by creating a pull request to the Related Websites Sets JSON file in GitHub.
- Browser Support: Currently supported only by Chromium-based browsers.
- Storage Access API:
- Functionality: Allows embedded widgets to request storage access from the user.
- Mechanism: The widget calls
requestStorageAccessto prompt the user. - Outcome: With user permission, the widget can access unpartitioned storage.
- Use Cases: When a user has previously interacted with the widget provider in a top-level context (e.g., logged in or set payment preferences).
- Browser Support: Works across devices and latest browser versions.
- Federated Credential Management (FedCM):
- Functionality: Enables users to sign in using account information from identity providers.
- Customization: Allows customization of the user identity experience (UI modes, prompt configuration).
- Trust Signal: An active FedCM session serves as a trust signal for the Storage Access API, granting automatic storage access without an additional user prompt.
- Use Cases: Identity payments and content providers.
- Browser Support: Not yet baseline; actively being implemented by other browsers.
Industry Adoption and Real-World Examples
- General Trend: Industry leaders recognize the importance of balancing privacy and user experience.
- KG Media (Indonesia): Integrated Related Websites Sets and FedCM for Google Identity Services to maintain a seamless, personalized user experience while respecting user privacy. Reaches over 70 million monthly active users.
- Seznam (Czech Republic): Integrated FedCM to allow users to sign in to e-shops on their partner's platform, resulting in increased user sign-in rates. Reaches over 90% of the Czech population.
- Tray (Brazil): Transitioned third-party plugins to CHIPS and updated internal applications to be first-party to each other. Prototyped and validated the CHIPS solution in a 15-day sprint with two developers.
Conclusion
The transition to a cookieless web requires developers to audit their solutions, understand the context in which their widgets operate, and adopt Privacy Sandbox APIs. CHIPS, Related Website Sets, the Storage Access API, and FedCM offer viable alternatives for maintaining functionality while enhancing user privacy. Industry leaders are already demonstrating the positive outcomes of adopting these new approaches. The key takeaway is to proactively test sites, transition to these APIs, and contribute to building a more privacy-respecting internet.
AI summaries can miss context or contain errors. Check important details against the original video.