F5 eBPF Observability: Real-Time Traffic Visibility Dashboard Demo
By F5 DevCentral Community
F5 eBPF Observability (EOB) Demonstration: Packet Capture in Kubernetes
Key Concepts:
- eBPF (extended Berkeley Packet Filter): A Linux kernel technology enabling safe, dynamic execution of programs within the kernel without modification or modules.
- EOB (F5 eBPF Observability): A platform leveraging eBPF for real-time visibility into Kubernetes and OpenShift environments.
- Directive: A set of instructions for EOB agents defining data collection parameters.
- Stream: A durable message store containing data collected by EOB agents based on a directive.
- Cluster Directive: A directive created by administrators with cluster-wide resource access.
- Arbback: An authentication function leveraging oAuth proxy (not enabled in this demo).
1. Introduction to F5 eBPF Observability (EOB)
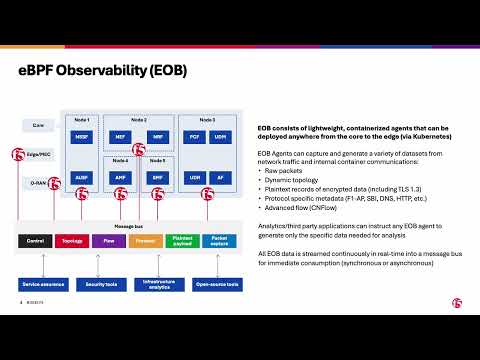
The demonstration focuses on utilizing the F5 EOB dashboard to capture network packets within a Kubernetes environment. EOB leverages the power of eBPF, a high-performance Linux kernel capability. eBPF allows programs to run within the kernel sandbox without requiring kernel source modifications or loading kernel modules. This provides full visibility into processes, containers, and network packets without traditional instrumentation or agents. EOB consists of lightweight, containerized agents deployable in Kubernetes or OpenShift. These agents can capture diverse datasets, including network traffic, container communications, raw packets, dynamic topology, encrypted data records, protocol metadata, and advanced flow metrics. A key feature is the ability to specify exactly the data needed for analysis, optimizing resource usage. All collected data is streamed in real-time to a message bus for immediate consumption.
2. Creating a Directive for DNS Packet Capture
The demonstration centers on creating a directive to capture DNS packets. A directive is defined as a sequence of tasks and conditions that dictate data collection and publishing. The process involves the following steps:
- Accessing the Directives Page: The demonstration begins on the directives page within the EOB dashboard.
- Creating a New Directive: Selecting "Create Directive" opens a side menu for parameter input.
- Task Selection: The capture task is set to "Packet Capture."
- Filtering: A filter is applied to capture only DNS traffic by specifying port 53.
- Publishing: The publish task defaults to "Stream," with options to customize the stream name and manage data deletion upon directive removal (data deletion is enabled in this example).
- Conditions: Conditions are used to refine data collection. The demonstration utilizes "Process Name" and sets the value to "coredns." The regular expression option is left disabled.
- Metadata: The namespace is selected as "kube-system." When Arbback is enabled, users would only see namespaces they are assigned to.
- Directive Creation: Clicking "Create Directive" initiates the directive deployment.
3. Verifying Directive Deployment and Observing Data Streams
After creating the directive, the demonstration focuses on verifying its deployment and observing the captured data:
- Directive Status: Initially, the directive status is "Not Ready." Hovering reveals the reason – in this case, the DaemonSet is not yet fully deployed.
- Stream Status: Once the directive reaches "Running" status, the "Streams" tab displays the data collection stream. Information displayed includes stream status ("Live"), stream name, namespace, storage location, message count, byte count, and rate per second (over a 30-second period).
- Capture Limits: The demonstration highlights cluster administrator-defined data capture limits: a maximum of 10 million messages, 1 gigabyte of data, and a 24-hour capture duration.
4. Analyzing Captured Data with the Packet Viewer and PCAP Export
The captured data can be analyzed in real-time:
- Packet Viewer: Clicking the "Shark Fin" icon opens a packet viewer interface resembling Wireshark, allowing basic filtering by protocol, source, and destination. It is noted that this is not a full Wireshark implementation.
- PCAP Export: The "Dump PCAP" option allows exporting the captured data to a PCAP file for analysis with a full-featured Wireshark installation on a local machine.
5. Directive Management: Editing, Pausing, Resuming, and Deleting
The demonstration covers directive management options:
- Editing: Directives can be edited to modify data capture parameters. Changes are reflected in the captured data after saving.
- Pausing/Resuming: Directives can be paused to temporarily halt data collection and resumed to restart it.
- Deleting: Deleting a directive also deletes the associated stream (due to the enabled deletion option).
6. Cluster Directives for Administrative Access
The demonstration contrasts regular directives with cluster directives:
- Cluster Directive Creation: Administrators can create cluster directives via the "Cluster Directives" tab.
- Deployment Options: Cluster directives offer deployment options for worker nodes (with and without taint tolerance) and master nodes (with and without taint tolerance).
- Use Case: Cluster directives are suitable for troubleshooting communication between pods in different namespaces, a task requiring cluster-wide visibility.
7. Technical Details & eBPF Capabilities
The demonstration emphasizes the power of eBPF: "Because eBPF runs at the host kernel level, we have total visibility into all processes running in every container within every pod within every name space in the cluster." This eliminates the need for complex instrumentation and provides a comprehensive view of the containerized environment.
8. Conclusion
“With F5’s EVPF observability, you now have real-time visibility and observability into your telco or enterprise-based container environment.” F5 EOB, powered by eBPF, provides a robust and efficient solution for real-time observability in Kubernetes and OpenShift environments, enabling proactive troubleshooting and performance optimization. The platform’s flexibility, through directives and streams, allows for targeted data collection and analysis, maximizing resource utilization and minimizing overhead.
Chat with this Video
AI-PoweredLoad the transcript when you're ready to chat so the initial page stays lighter.
Related Videos

Learning k8s - ep 6 - KCNA exam-prep app is live!
F5 DevCentral Community

Multi‑Cluster Kubernetes App Delivery Made Simple with F5 BIG‑IP CIS & Nutanix Kubernetes Platform
F5 DevCentral Community
F5 eBPF Observability: Kernel-Level Observability for Modern Applications
F5 DevCentral Community

Open Source Friday with Cilium
GitHub