F5 Distributed Cloud API Security: Comprehensive Summary
Key Concepts:
- APIs (Application Programming Interfaces)
- Hybrid App Deployment Model
- Multi-Lens API Discovery
- API Attack Surface Mapping/Crawling
- Runtime API Traffic Inspection
- Code Scanning
- API Governance
- Inline Protections
- Anomaly Detection
- API Inventory (Inventoried, Discovered, Shadow)
- Open API Specification (OAS)
- Schema Validation
- API Endpoints Dashboard
- Sensitive Data Discovery
- API Risk Score
- Vulnerability Management
- Remediation Recommendations
1. The Pervasiveness and Growth of APIs:
- APIs power a vast array of applications, from banking and ride-sharing to weather apps.
- Mobile apps often rely on APIs from multiple sources (e.g., edge, data center, cloud, CDN).
- API requests constitute 83% of all internet traffic.
- API traffic is growing 300% faster than overall web traffic.
- The number of APIs in production is projected to increase exponentially, potentially reaching 500 million to 1 billion by 2030 (according to F5's Office of the CTO estimates).
2. The Challenge of API Security in Hybrid Environments:
- Nearly 90% of organizations operate a hybrid app deployment model (2024 F5 State of Application Strategy Report).
- 41% of organizations manage at least as many APIs as they do apps.
- This creates a large and complex attack surface, where complexity is the enemy of security.
3. F5 Distributed Cloud API Security: A Comprehensive Solution:
- Provides comprehensive API security from development time to runtime.
- Offers multi-lens discovery, governance, detection, and protection capabilities.
- Aims to enable organizations to manage and secure their API ecosystems effectively.
4. Multi-Lens API Discovery:
- F5 Distributed Cloud offers true multi-lens API discovery through code scanning, traffic inspection, and crawling.
- This allows building a complete inventory of known and unknown APIs.
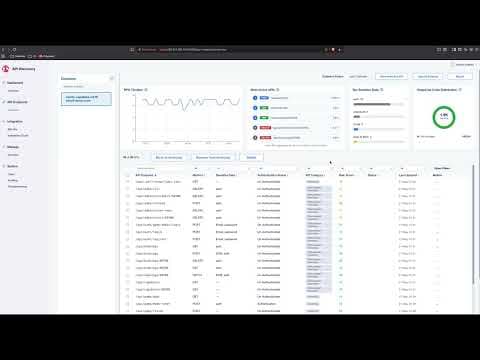
- The API Endpoints Dashboard provides a visual rendering of APIs, color-coded to differentiate between inventoried, discovered, and shadow APIs.
- The "Discover" tab in the endpoint details section shows everything learned about the endpoint, including request/response data and authentication information.
- The service automatically generates an Open API Specification (OAS) that outlines the structure, endpoints, and data models of the API.
- The OAS serves as a blueprint for schema validation, ensuring API requests and responses adhere to the defined standard.
5. Centralized Dashboards and Real-Time Security Visibility:
- Data-rich dashboards deliver a centralized, real-time, security-focused view of the API landscape.
- Provides detailed information about security events and a quick view of the API inventory organized by classification.
- The API Endpoints Dashboard provides information such as top attacked APIs, top sensitive data discovered, total API calls by response code, and most active APIs.
6. Detailed API Inventory and Security Posture Analysis:
- The table view presents an essential view of the API inventory.
- Information includes sensitive data types found, threat level based on attack traffic volume, authentication status, API category, and calculated risk score.
- Clicking on an endpoint reveals details related to its health, behavior, authentication (learned and inventory specification), and security posture.
- The security posture tab shows active and archived vulnerabilities with detailed descriptions and remediation recommendations.
- A link to the evidence takes you to the request monitoring tab, filtered to the request ID, allowing detailed investigation of the vulnerability as seen in traffic.
7. Security Event Analysis and Threat Identification:
- The "Show Security Events" option provides deep insights into the security of an API.
- Enables identification of potential threats, malicious activity, and vulnerabilities.
- Facilitates proactive security measures and enhances incident response.
8. Key Arguments and Perspectives:
- APIs are the lifeblood of modern applications.
- Their complexity and rapid proliferation create significant security challenges.
- Comprehensive API security is essential for organizations to innovate with confidence.
9. Notable Quotes:
- "Complexity is the enemy of security."
- (Implied) APIs are the lifeblood of modern applications.
10. Synthesis/Conclusion:
F5 Distributed Cloud API Security offers a comprehensive solution to address the growing challenges of API security in hybrid and multi-cloud environments. By providing multi-lens discovery, robust governance, real-time detection, and comprehensive protection, it empowers organizations to manage and secure their API ecosystems effectively, enabling them to innovate with confidence. The platform's focus on visibility, detailed analysis, and actionable insights allows for proactive security measures and efficient incident response.
AI summaries can miss context or contain errors. Check important details against the original video.