Key Concepts
- App Gateway v2 Network Isolation: Separates client data plane traffic from Azure control plane traffic.
- Azure Control Plane (ARM): The management layer of Azure responsible for creating, configuring, and managing resources.
- Data Plane: The path that client traffic takes to reach the application.
- Gateway Manager: A component of the Azure control plane that manages App Gateway.
- Public IP vs. Private IP: Public IPs are accessible from the internet, while private IPs are only accessible within a virtual network or connected networks.
- Private Endpoint: A network interface that uses a private IP address from your virtual network to connect privately and securely to an Azure service.
- Network Security Group (NSG): Azure's firewall that controls network traffic in and out of Azure resources.
- VNET (Virtual Network): A logically isolated network in Azure.
- Subscription Flag: A setting at the Azure subscription level that enables or disables the network isolation feature for new App Gateway deployments.
App Gateway Network Isolation Update: Deep Dive
Introduction
The video provides an update to the App Gateway, focusing on the new network isolation capabilities available in the v2 version. It builds upon the original deep dive released four years prior, highlighting the architectural changes and benefits of this update.
App Gateway Refresher
- App Gateway is a layer 7 load balancing solution deployed within a specific region and virtual network, residing in a dedicated subnet.
- It supports protocols like HTTP, HTTPS, HTTP2, and WebSockets, enabling features like URL-based redirection, rewrites, TLS termination, and session affinity.
- App Gateway can front traffic to VMs, App Services, or any IP address/FQDN reachable via IP path, including resources in peered VNETs or connected via Site-to-Site VPN or ExpressRoute.
- The video emphasizes the importance of using App Gateway v2, as v1 is deprecated and a migration script is available.
Front-End Configuration (Original v2)
- Traditionally, App Gateway v2 required a public IP address for client traffic and optionally supported a private IP address from the subnet.
- Private Link support was available, allowing private endpoints in other VNETs to connect without peering.
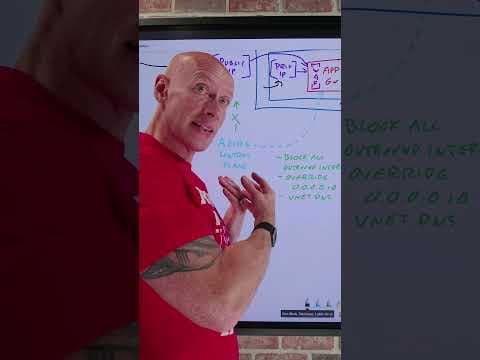
- Even when aiming for private-only deployments, the public IP was mandatory due to the Azure control plane (ARM) using the same endpoint for management traffic.
- Network Security Group (NSG) rules required allowing traffic from "GatewayManager" to support the control plane.
- App Gateway needed outbound internet access to communicate with the control plane, restricting the ability to block all outbound traffic or override the default internet route (0.0.0.0/0).
- Azure DNS (168.63.129.16) had to be used for resolving certain services like
azure.net.
New Network Isolated Architecture (v2)
- The new architecture separates client data plane traffic from the Azure control plane traffic.
- This separation removes the restrictions imposed by the shared endpoint, making the public IP optional and allowing for more granular network control.
- The feature is generally available (GA) but requires opting in via a subscription flag.
Subscription Flag: Enabling Network Isolation
- The "Enable application gateway network isolation" flag is found under "Preview Features" in the Azure subscription.
- Registering for the feature enables the new architecture for new App Gateway deployments.
- Unregistering the feature reverts to the old architecture for new deployments.
- Important: The flag only affects new deployments. Existing App Gateways are not modified.
Time-Based Architecture Selection
The video uses a timeline to illustrate how the flag affects architecture selection:
- Existing App Gateway (Before Flag): Uses the original architecture with a shared public IP for data and control plane traffic.
- Flag Enabled: No change to existing App Gateways.
- New App Gateway (After Flag): Uses the new network-isolated architecture.
- Flag Disabled: New App Gateways will revert to the original architecture.
Portal Experience with Network Isolation Enabled
- When creating a new App Gateway with the flag enabled, the front-end configuration offers complete choice: public IP only, private IP only, or both.
- The Azure control plane now uses a separate path, making the public IP optional.
- Restrictions related to outbound internet access, default internet route, and DNS resolution are removed.
- Even with a public IP, the previous restrictions no longer apply.
Tagging and Functionality
- The new architecture automatically adds a tag "enhancedNetworkControl: true" to the App Gateway resource. This tag is purely informational and has no functional impact.
Reason for the Flag: Private Endpoint Limitation
- The primary reason for the flag's existence is a current limitation: the new architecture does not yet support creating private endpoints.
- If private endpoint support is required, the flag must be disabled to create an App Gateway using the old architecture.
- The product team plans to lift this limitation in the future, potentially removing the need for the flag.
Key Benefits of Network Isolation
- Optional Public IP: The public IP address is no longer mandatory.
- Enhanced Network Control: Ability to block all outbound internet traffic, override the default internet route, and use the virtual network's DNS configuration.
- Security: Reduced attack surface by isolating the control plane.
Notable Quotes
- "The flag is controlling which architecture I use. That's all it's doing."
- "Turning on network isolation makes the public IP address optional because the control plane doesn't use it anymore."
Technical Terms Explained
- Layer 7 Load Balancing: Load balancing based on application-level data, such as HTTP headers and URLs.
- TLS Termination: Decrypting TLS (Transport Layer Security) traffic at the App Gateway, allowing it to inspect the content.
- Session Affinity (Cookie-Based Affinity): Directing requests from the same client to the same backend server.
- Private Link: A service that enables you to access Azure PaaS Services (for example, Azure Storage and SQL Database) and Azure hosted customer-owned/partner services privately from your virtual network. Traffic between your virtual network and the service travels the Microsoft backbone network.
Conclusion
The App Gateway network isolation update provides significant benefits by separating the client data plane from the Azure control plane. This separation makes the public IP address optional and allows for enhanced network control and security. The subscription flag controls which architecture is used for new deployments, with the primary reason for its existence being the current lack of private endpoint support in the new architecture. Users should consider their requirements for private endpoints when deciding whether to enable or disable the flag. Once the private endpoint limitation is lifted, the flag may become obsolete.
AI summaries can miss context or contain errors. Check important details against the original video.