Key Concepts
AI Agents, Autonomous Systems, Tasks, Tools, Memories, Zero Trust, Security Risks, Unauthorized Access, Data Leakage, Safety, Trust, Compliance, Governance, Evals, Risk Score, Enforcement, Observability, Authentication, Authorization, Approvals, User Identity Propagation, Thresholds, Metrics, Failure Rates, Anomaly Detection, Security Posture.
1. Introduction and Terminology (0:00-1:50)
- Main Topic: Defining AI agents and related components.
- Key Points:
- AI agents are autonomous systems capable of reasoning, creating workflows, and executing tasks.
- Tasks: Specific actions, potentially using LLMs, RAG, or tools.
- Tools: Functions for data retrieval from the internet, databases, or service APIs.
- Memories: Shared context between agents, tasks, and tools.
- Visual Representation: Multiple agents can access multiple tasks and tools, which interact with APIs and databases.
2. Security Risks in Current Agent Frameworks (1:50-3:00)
- Main Topic: Identifying security vulnerabilities in current AI agent implementations.
- Key Points:
- Most agent frameworks run as a single process, creating a "zero trust" issue.
- Tools require credentials (often service user credentials with super admin privileges) to access databases or APIs.
- Any tool within the process can potentially access credentials of other tools.
- Third-party libraries can access prompts and other sensitive data within the process.
- Agents interact with LLMs, which can be exploited if not secured.
- Agent autonomy introduces "unknown unknowns" due to their non-deterministic behavior.
- Attack vectors are higher in agents compared to traditional software.
3. Challenges Arising from Security Risks (3:00-4:25)
- Main Topic: Discussing the challenges related to security, safety, compliance, and governance in AI agents.
- Key Points:
- Improperly designed agents can lead to unauthorized access and data leakage.
- Unreliable models or compromised prompts can affect safety and trust.
- Compliance and governance are often overlooked during agent development.
- Example: A top-three credit bureau considers AI agents similar to human users, requiring onboarding, training, and adherence to regulations (e.g., California Consumer Privacy Act (CCPA), GDPR).
- Specific Details: Regulations dictate data access based on user consent, marketing restrictions, and regional data regulations.
4. Addressing Security Challenges: A Layered Approach (4:25-5:15)
- Main Topic: Proposing a multi-layered approach to address security challenges in AI agents.
- Key Points:
- No single solution exists; a layered approach is necessary.
- Three layers:
- Evals: Criteria for putting agents into production, including security and safety-focused evaluations.
- Enforcement: Implementation of security measures to enforce policies.
- Observability: Monitoring agent behavior in real-world scenarios to react to anomalies.
5. Evaluation (Evals) Layer (5:15-7:30)
- Main Topic: Discussing the importance of evaluations (Evals) for AI agent security and safety.
- Key Points:
- Traditional software development practices (test coverage, vulnerability scanning, penetration testing) should be applied to AI agents.
- Evals should cover use cases, ground truth, third-party LLM vulnerabilities, and prompt injection.
- Specific Evals:
- Data Leakage: Preventing unauthorized access to sensitive information.
- Unauthorized Actions: Ensuring actions are performed by the right person with the right permissions.
- Runaway Agents: Testing for infinite loops caused by bad prompts or agent limitations.
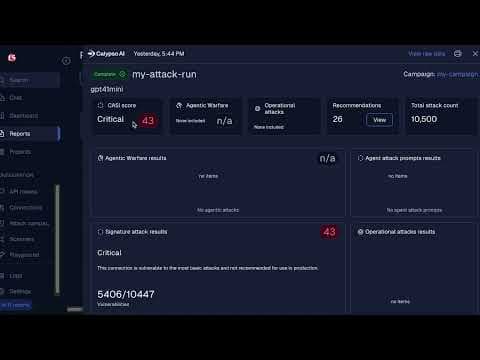
- Goal: Generate a risk score to determine if an agent can be deployed to production.
6. Enforcement Layer (7:30-9:30)
- Main Topic: Discussing the enforcement layer, focusing on authentication and authorization.
- Key Points:
- Enforcement is crucial for a good risk score.
- Agents operate in a "zero trust" environment.
- Authentication and Authorization:
- Essential for preventing impersonation and data theft.
- Agents have their own roles, and access must be controlled accordingly.
- User identity must be propagated across all tasks and tools to enforce policies at the point of data access.
- Approvals:
- Automated approval workflows can be implemented using agents, with human-in-the-loop for exceeding thresholds.
7. Observability Layer (9:30-11:00)
- Main Topic: Discussing the importance of observability for monitoring AI agent behavior.
- Key Points:
- Models, frameworks, and third-party libraries evolve rapidly.
- User inputs can vary significantly, affecting agent responses.
- Monitoring is needed to track Personally Identifiable Information (PII) and confidential data being sent out.
- Thresholds and Metrics:
- Define acceptable failure rates and create alerts for exceeding them.
- Anomaly Detection:
- Monitor agent behavior to identify deviations from accepted boundaries.
- Integrate with security posture for near real-time assessment of agent performance.
8. Recap and Call to Action (11:00-11:45)
- Main Topic: Summarizing the key takeaways and inviting collaboration.
- Key Points:
- Three layers: preemptive evals, proactive enforcement, and observability.
- Open-sourced solution: Page. A for AI security and compliance.
- Seeking design partners and contributors.
- Contact Don B at boscat page. or via LinkedIn.
9. Synthesis/Conclusion
The video emphasizes the critical need for security and safety in AI agents, highlighting the unique challenges posed by their autonomous nature and complex interactions. It advocates for a layered approach encompassing evaluations, enforcement, and observability to mitigate risks and ensure responsible deployment of AI agents in enterprise environments. The speaker invites collaboration on the open-source project Page. A to advance AI security and compliance.
AI summaries can miss context or contain errors. Check important details against the original video.